 34:55
This recording is not available yet.
Categories
About this session
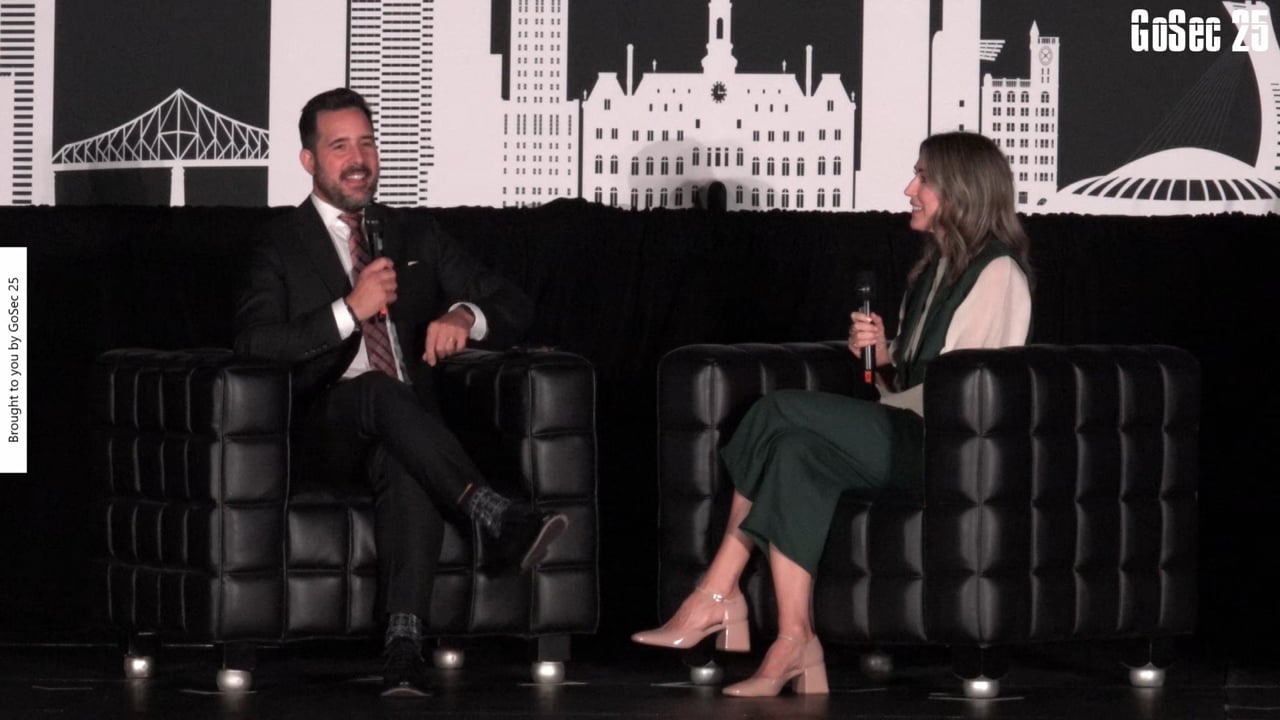
A moderator traces the red team/blue team terminology to 1960s US military exercises, then runs a four-person panel identified by color-coded caps: Jasmin, a full-time bug bounty hunter and former NASDAQ security director; Martin Dubé, co-founder of offensive-security firm Corsek; Patrick Mathieu, who built DoorDash's product security program and co-founded Hackfest; and Mathieu Saulnier, a blue-team veteran now product manager for BloodHound Community Edition at SpecterOps. They contrast pentesting (breadth, finding vulnerabilities), red teaming (a defined objective, MITRE ATT&CK-style TTPs, meant to test incident response), and purple teaming (collaborative testing of detection playbooks). Recurring themes include matching engagement intensity to a client's maturity, valuing the report over the exploit, honoring both red and blue wins, and using honeytokens and proactive threat hunting. A long discussion covers why blue teams share far less than red teams versus Europe's more mature trust groups, and whether red and blue should report to the same leadership. The panel closes on AI: report writing, red-team code generation via coding assistants, automated CVE-to-exploit tools, a Gemini prompt-injection technique, and blue-team automation of access approvals.
Key takeaways
- Run purple team exercises that pair a red action with immediate blue feedback, since the real value is testing whether detection playbooks fire, not whether the attacker technically succeeds.
- Test your EDR or antivirus against a real malware sample at least once; the panel's informal show of hands found almost no one in the room had actually done this.
- Deploy honeytokens (decoy accounts, machine credentials or files that no legitimate process should ever touch) as a cheap, high-fidelity way to detect lateral movement and tools like BloodHound.
- Keep red and blue team functions under the same reporting line, ideally near the CISO, so incentives align and findings actually get remediated rather than becoming inter-team point-scoring.
- When using an LLM for detection-engineering or exploit code, ground it in a reference corpus (e.g. a cloned Sigma or YARA rule set) and break complex requests into function-by-function prompts rather than one large prompt.
Speakers
Julien Turcot
Julien Turcot has spent more than two decades on the front lines of cybersecurity, navigating boardrooms and breach rooms with equal precision. As Senior Vice President of Sales & Marketing at GoSecure, he has helped organizations across North… Read moreRead less
Julien Turcot has spent more than two decades on the front lines of cybersecurity, navigating boardrooms and breach rooms with equal precision. As Senior Vice President of Sales & Marketing at GoSecure, he has helped organizations across North America strengthen their defenses, respond to crises, and turn security from a cost into a competitive advantage. A seasoned strategist, relentless dealmaker, and natural storyteller, Julien blends technical insight with a human touch, proving that in a world of constant digital threats, relationships remain the most powerful firewall.
Jasmin Landry
Jasmin Landry is a seasoned ethical hacker and full-time bug bounty hunter who has reported hundreds of security vulnerabilities to some of the world’s largest tech companies. After years leading cybersecurity efforts as Senior Director of… Read moreRead less
Jasmin Landry is a seasoned ethical hacker and full-time bug bounty hunter who has reported hundreds of security vulnerabilities to some of the world’s largest tech companies. After years leading cybersecurity efforts as Senior Director of Information Security at Nasdaq, Jasmin returned to his roots in hacking — now focusing exclusively on uncovering critical bugs through platforms like HackerOne and Bugcrowd. Recognized at multiple live hacking events for top findings, he brings a sharp eye for unexpected issues and a deep understanding of modern attack surfaces. He’s also a co-leader of OWASP Montréal and an active voice in the security research community while being a member of the HackerOne Hacker Advisory Board.
Mathieu Saulnier
Mathieu Saulnier is a cybersecurity leader with 20+ years in Threat Research, Detection Engineering, Threat Hunting, and Incident Response. He has led diverse, global teams to success and shared his expertise on stages at Derbycon, SANS Summits… Read moreRead less
Mathieu Saulnier is a cybersecurity leader with 20+ years in Threat Research, Detection Engineering, Threat Hunting, and Incident Response. He has led diverse, global teams to success and shared his expertise on stages at Derbycon, SANS Summits, RSAC, SecTor, and BSides worldwide. A dedicated community mentor with DEF CON’s Blue Team Village and co-organizer of NorthSec, DEATHcon and SkiCon, Mathieu now serves as Product Manager for BloodHound Community Edition, empowering attackers and defenders to audit and secure complex environments.
Patrick Mathieu
Patrick est cofondateur du Hackfest.ca et s’implique dans le domaine de la sécurité informatique depuis plus de 20 ans et a été Senior Manager Product Security chez Doordash et anciennement Offensive Security Lead (Red team) chez LogMeIn et Duo… Read moreRead less
Patrick est cofondateur du Hackfest.ca et s’implique dans le domaine de la sécurité informatique depuis plus de 20 ans et a été Senior Manager Product Security chez Doordash et anciennement Offensive Security Lead (Red team) chez LogMeIn et Duo Security. Patrick possède un Bacc. et un DEC en informatique et de plus, il a toujours été actif dans la communauté et dans les événements de sécurité. En plus d'avoir un background en test d'intrusion applicatif et de sécurité offensive, il a agi en tant que conférencier depuis plus de 10 ans et a offert des ateliers aux DEF CON, Blackhat, DerbyCon et plusieurs autres événements locaux au Québec tels que la JiQ, LesAffaires, Web à Québec et plusieurs universités et cégeps. En plus de son implication dans la communauté de sécurité informatique, il fut conseiller sur le comité de la première politique de cybersécurité de la province de Québec et participant au plus grand podcast de sécurité francophone La French Connection (https://securite.fm).
Martin Dubé
Martin est président et cofondateur de Corsek, une entreprise dédiée à offrir des services de pointe et modernes en sécurité offensive (Pentest, Purple Team, Red Team). Fort de plus de dix ans d’expérience concrète dans le domaine, Martin a… Read moreRead less
Martin est président et cofondateur de Corsek, une entreprise dédiée à offrir des services de pointe et modernes en sécurité offensive (Pentest, Purple Team, Red Team). Fort de plus de dix ans d’expérience concrète dans le domaine, Martin a développé une approche de leadership axée sur la collaboration. Son parcours compte plus de 100 missions de consultation, où il a réalisé des tests de sécurité dans de nombreux secteurs d’affaires, ainsi que d’un mandat de près de cinq ans à titre de leader technique et gestionnaire au sein d’une grande organisation. Animé par la volonté de maximiser le potentiel des talents en sécurité offensive, il est convaincu que la force collective dépasse la somme des compétences individuelles. Il porte un intérêt particulier au Purple Teaming, qu'il considère comme l'incarnation parfaite de cette philosophie collaborative et une source de valeur exceptionnelle pour les organisations.