 35:14
This recording is not available yet.
Back to the Basics – Navigating the Evolving Cybersecurity Landscape with Some Tried and Test Approaches
Download resourcesCategories
AI & Emerging TechnologyAI GovernancePrivacy & Data ProtectionData Loss PreventionPeople, Culture & Careers
Sponsored by
About this session
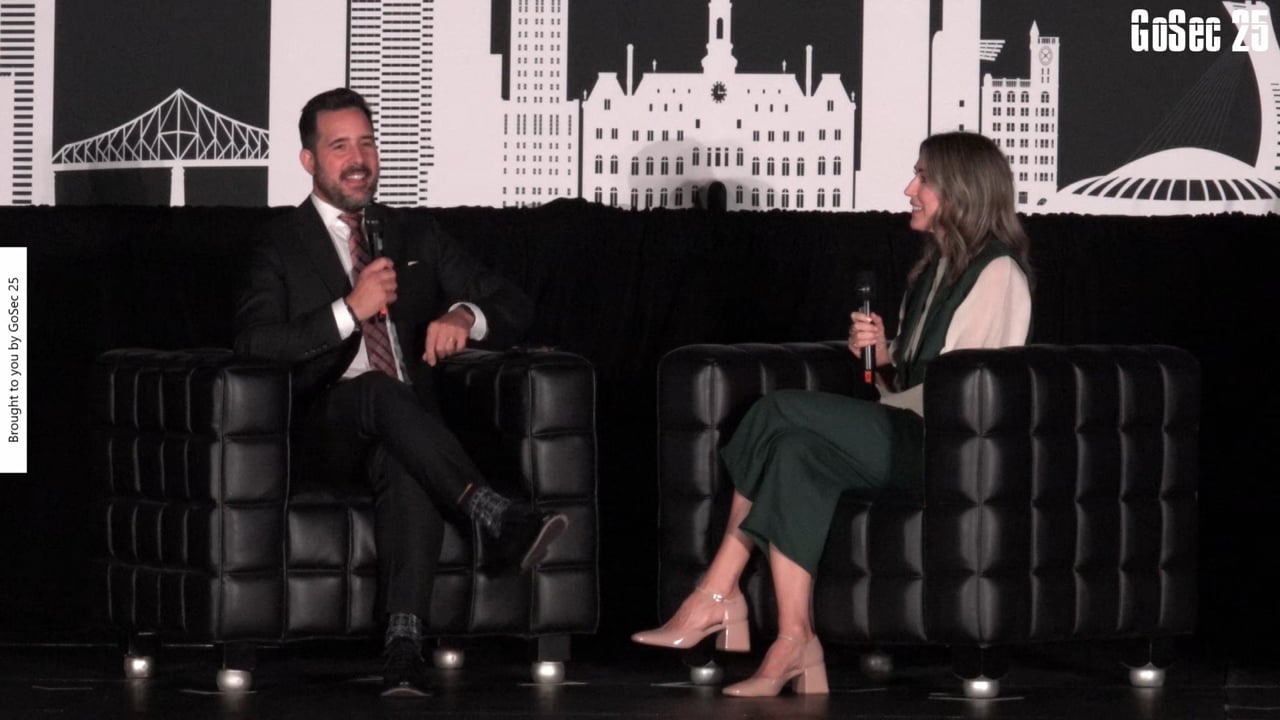
Cedric Brossard, PwC's Montreal cybersecurity practice director and former CISO at Transat and FIERA Capital, and Olivier Gaston, PwC Senior Director, argue that securing each new wave of technology, from virtualization and SaaS to cloud and now generative AI, comes down to three familiar pillars: organization-wide awareness, an integrated risk model that quantifies financial impact for board-level risk-appetite decisions, and a deliberate technology-adoption model, since security teams have historically had to react to urgent threats, citing the ILOVEYOU virus, rather than plan ahead. They apply this framework to generative AI as a live case study: treat any GenAI tool as another application requiring data protection, since SaaS-based models amount to shadow IT and every prompt sent out is potential data exfiltration; extend DLP controls to text sent to AI tools the way code repositories are already monitored; and route AI-generated code through the same security pipeline as human-written code. They cite the NIST AI Risk Management Framework as an early governance reference and note regulation lags vendor self-regulation driven by reputational risk. A brief Q&A closes the session with an offer to share the deck.
Key takeaways
- Treat any SaaS-based generative AI tool as shadow IT and a new application requiring data protection controls, not a special exception to existing policy.
- Extend DLP monitoring to text sent into AI prompts the same way code repositories are already watched, since a full document uploaded to a chatbot can leak into the vendor's training data.
- Route any AI-generated code through the normal secure development pipeline before deployment; it can contain flaws or vulnerabilities just like human-written code, even when it looks correct.
- Quantify new-technology risk in financial-impact terms at the product, application and vendor level, and use that quantification to earn board-level buy-in for risk tolerance decisions rather than relying on generic warnings.
- Build security awareness before the business adopts a new technology, not after; security teams that only react once a threat is already live cannot shape safe adoption.
Speakers
Cedric Brossard
With more than 25 years of experience in business, IT and cybersecurity consulting, Cédric Brossard has helped international organizations with their most challenging business and digital transformation opportunities. Cédric was responsible for the… Read moreRead less
With more than 25 years of experience in business, IT and cybersecurity consulting, Cédric Brossard has helped international organizations with their most challenging business and digital transformation opportunities. Cédric was responsible for the development of the IT strategy, infrastructure and security practices in Europe and North America for Accenture, KPMG and IBM. He was also CTO of Accor group, global CISO of Fiera Capital and Air Transat. Cédric brings his strengths in diagnostic and strategic planning, formulating innovative ideas and options to design and implement original solutions to improve operational excellence, reduce risks and costs or help launching new products, services and business models.