 34:55
This recording is not available yet.
GoCast Podcast: Julien Turcot & Patrick Garrity (Vulncheck)
Download resourcesCategories
About this session
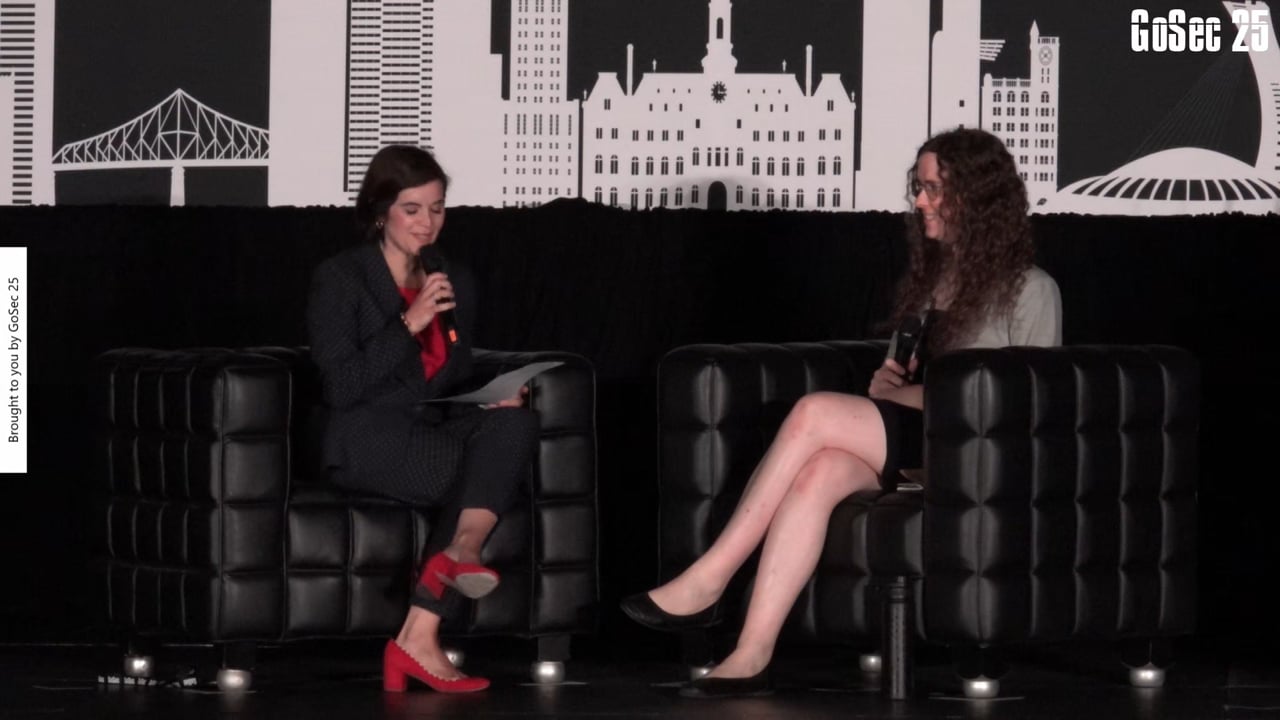
In this GoCast interview recorded on the show floor at GoSec 2025, host Julien Turcot talks with Patrick Garrity, a security researcher at VulnCheck, ahead of Garrity's keynote on exploitation trends. Garrity traces his path through product security roles at companies including Duo Security, Censys and Blumira before moving into vulnerability and exploit intelligence, and argues for faster, more open disclosure of what is being actively exploited so defenders can patch and deploy mitigations sooner. He calls for closer collaboration between red and blue teams, and for security to engage more directly with the developers building the technology it protects. Asked about artificial intelligence, he is cautious: useful for narrow tasks like writing a script, but surrounded by marketing and hype, and often applied where plain automation would do just as well. He previews his keynote, which visualizes first-half-2025 exploitation data by product category, from edge devices to content management systems to IoT. The conversation closes on a personal note, about skateboarding in Montreal and a cousin he lost earlier in the year.
GoCast is hitting the road and heading straight to the Main Stage at GoSec 2025! Get ready for a series of exclusive mini-interviews with some of the brightest minds in cybersecurity. Experience the unique energy of GoCast live at the heart of the conference — short, dynamic, and always captivating conversations that capture the ideas, trends, and voices shaping the future of cybersecurity.
Key takeaways
- Disclose exploitation information (what, when, how) as fast and openly as possible so defenders know to patch or add mitigating controls.
- Build working relationships between red and blue teams; use offensive testing to validate whether preventive controls actually hold.
- Categorize what is being exploited (edge devices, CMS, IoT) so the right internal team owns patching and mitigation for each.
- Treat AI as useful for narrow, well-defined tasks; verify claims before trusting AI-generated output, and default to plain automation where it is sufficient.
- Security teams should spend more time talking directly with the developers and business teams building the technology, not just with each other.
Speakers
Patrick Garrity
Patrick Garrity is a security researcher at VulnCheck where he focuses on vulnerabilities, vulnerability exploitation and threat actors. Patrick has spent the last decade helping building Cybersecurity companies including Duo Security, Censys… Read moreRead less
Patrick Garrity is a security researcher at VulnCheck where he focuses on vulnerabilities, vulnerability exploitation and threat actors. Patrick has spent the last decade helping building Cybersecurity companies including Duo Security, Censys, Blumira, Nucleus Security and VulnCheck.