 41:02
This recording is not available yet.
Malicious Masquerade: Preventing Account Takeover Attacks
Download resourcesCategories
About this session
Aparna Rayasam, head of application security at Akamai, walks through account takeover as a business run by criminals and how to make it unprofitable. She defines ATO and credential stuffing, now spreading from banking to media, gaming and retail, with more than 100 billion stuffing attempts seen by Akamai over two years. Using a kill-chain model, she follows the attacker: buying combo lists, reconnaissance of login portals and subdomains, harvesting through phishing, infostealers, exposed files and criminal marketplaces that also sell device fingerprints; validation at scale with tools such as SentryMBA and Sniper that bypass rate limits and CAPTCHAs; proxies and botnets, including hijacked IoT devices as in Mirai; and finally monetisation through fraud, data theft or business email compromise. A real attack on a bank shows adversaries pivoting across login workflows and returning weeks later against mobile endpoints. She presents Akamai's Bot Manager and Account Protector, stressing first-party edge data and behavioural risk scores, then reframes defence around economics: raise the attacker's hardware, credential and human costs at each stage until they move to an easier target.
Account takeovers (ATOs), in which criminals impersonate legitimate account owners to take control of an account, cost businesses time, money and often, their reputations. In addition to credential stuffing, criminals are making bots more sophisticated and using human “CAPTCHA farms” to be more effective at account takeovers. Discover the techniques cybercriminals are using to steal sensitive data and how their tactics are evolving. Learn the multiple security capabilities that may counter ATO attempts during each stage of the bot kill chain. The speaker will explain the economics of these malicious activities and how to prevent your own company’s data from being compromised.
Key takeaways
- Assume your users reuse passwords: you must defend against other companies' breaches, because stuffing tools are built to replay them against you.
- Map mitigations to each kill-chain stage (acquisition, reconnaissance, validation, exploitation) instead of relying on a single login-page control.
- Think of the attacker as a business: raise their hardware, proxy, credential-purchase and CAPTCHA-farm costs and lower their success rate until your site is not worth the spend.
- Expect pivots: after a bot attack is blocked, adversaries return against other workflows and mobile endpoints, so protect the whole company, not one endpoint.
- For human-driven takeovers with valid credentials, rely on device fingerprints, network reputation and login-behaviour anomalies such as impossible travel, combined into a risk score.
Speakers
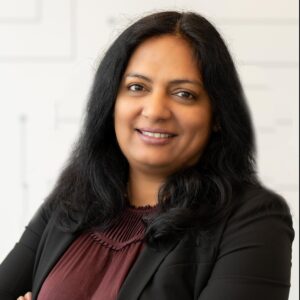
Aparna Rayasam
Aparna Rayasam, Senior Vice President and General Manager, Application Security, is responsible for Akamai's Application Security business within the Security Technology Group. She is responsible for leading product management, business development… Read moreRead less
Aparna Rayasam, Senior Vice President and General Manager, Application Security, is responsible for Akamai's Application Security business within the Security Technology Group. She is responsible for leading product management, business development, engineering, research, data science, and operations for Akamai’s Application Security portfolio. Previously, she served as Vice President, Web Security Engineering, where she was responsible for all research and development of Akamai’s web security portfolio. In her career at Akamai, she has held several engineering and product leadership roles and was responsible for the development and launch of several Akamai products, including Akamai’s award-winning web application firewall, Kona Site Defender, Client Reputation, and Bot Manager. Prior to joining Akamai in 2006, she held several engineering leadership roles at Oracle and Adobe. Rayasam holds a Bachelor of Engineering degree in Information Science from Bangalore University, India. She has also participated in several executive education programs at MIT’s Sloan School of Management and is a board member of several nonprofit organizations in the Boston metropolitan area.