 51:10
This recording is not available yet.
Categories
About this session
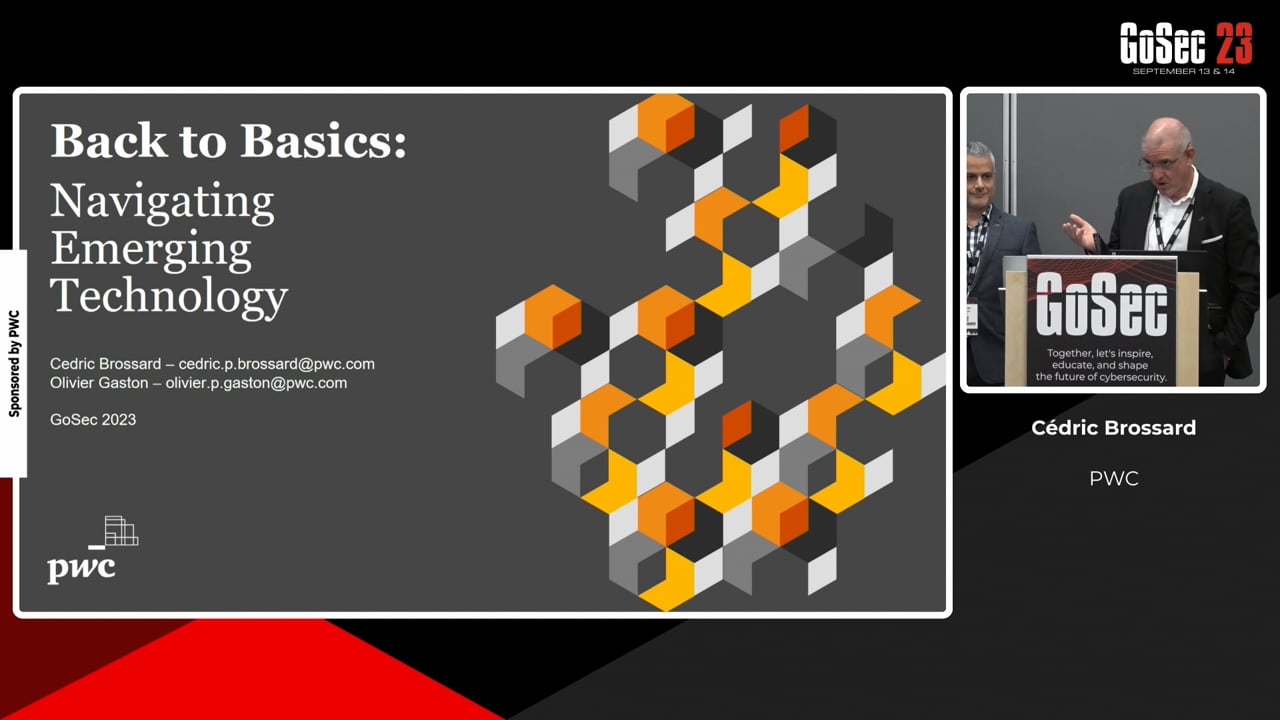
Cédric Brossard, a former Big Four and IBM consultant who has since held CISO roles at Fiera Capital and Air Transat, makes the case that security is a business problem and that governance, risk and compliance (GRC) only delivers when risk is expressed in dollars. Speaking half in English and half in French, he first defines GRC as decision-making that leads to compliance, not the reverse, sets it apart from SAP-style financial GRC, and walks through a five-level maturity model where a show of hands puts most of the room at spreadsheets and manual processes. The second half turns to cyber risk quantification with the FAIR method: why high/medium/low heat maps cannot rank a likely-but-small risk against a rare-but-huge one, how loss frequency and loss magnitude, including secondary losses like class actions, are estimated as ranges, and how insurer data from Marsh and Lloyd's narrows them. A case study shows an ageing ERP with a 5.8 million exposure where patching plus encryption costs about one million and removes most of it. Q&A covers time to maturity, small companies, cyber insurance exclusions and breach coaches.
No Description
Key takeaways
- Start GRC with governance: write down who decides what, at which level, and define risk appetite, tolerance and capacity as three distinct numbers.
- Replace high/medium/low heat maps with FAIR scenarios on your top ten crown jewels, estimating loss frequency and loss magnitude as a range, not a point.
- Include secondary losses (class actions, regulatory fines, lost customers) in each scenario; they can dwarf the ransom and recovery cost.
- Use the quantified range to justify projects: if patching plus encryption costs one million against a five-million exposure, the decision holds even with 50 percent error.
- Treat cyber insurance as one option alongside accept, mitigate and compensating controls, and expect rising premiums and exclusions for unpatched or known-vulnerable systems.
Speakers
Cedric Brossard
With more than 25 years of experience in business, IT and cybersecurity consulting, Cédric Brossard has helped international organizations with their most challenging business and digital transformation opportunities. Cédric was responsible for the… Read moreRead less
With more than 25 years of experience in business, IT and cybersecurity consulting, Cédric Brossard has helped international organizations with their most challenging business and digital transformation opportunities. Cédric was responsible for the development of the IT strategy, infrastructure and security practices in Europe and North America for Accenture, KPMG and IBM. He was also CTO of Accor group, global CISO of Fiera Capital and Air Transat. Cédric brings his strengths in diagnostic and strategic planning, formulating innovative ideas and options to design and implement original solutions to improve operational excellence, reduce risks and costs or help launching new products, services and business models.