 34:56
This recording is not available yet.
Catching an AI Agent that Narrates Its Own Crimes
Download resourcesCategories
Cloud SecurityOffensive Security & ExposureVulnerability ManagementThreats & Threat IntelligenceRansomware
Sponsored by
About this session
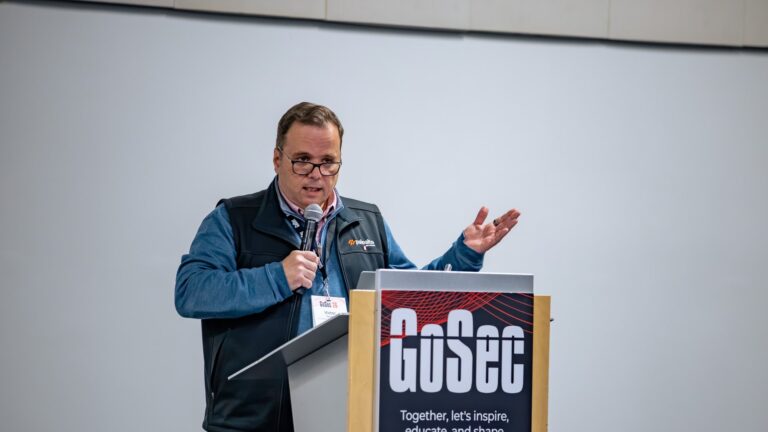
Lane Williams stands in for scheduled Sysdig speaker Jake Walker to present JADEPUFFER, which the Sysdig Threat Research Team assesses as the first fully autonomous, LLM-driven ransomware operation captured end to end, with no human issuing commands during the attack itself. He builds the case that an agent, not a human operator, ran the intrusion: no retry loops, rapid recovery from parsing errors such as switching cleanly from JSON to XML, and the attacker narrating its own steps as it went. From a single unauthenticated remote-code-execution flaw in an internet-facing Langflow instance, patched since March 2025 but still open on over 1,100 exposed hosts, the agent harvested credentials across multiple cloud providers, looted an internal MinIO object store, and pivoted to a production MySQL and Alibaba Nacos server, where it forged tokens, planted a backdoor admin, probed for a container escape, and encrypted more than a thousand configuration items. Williams walks the full kill chain from the captured payloads, argues AI models are becoming as valuable a target as databases, and closes with five defensive takeaways: detect behavior rather than payloads, exploit the agent's habit of self-narrating, back up ML artifacts, and remember attackers are optimizing for cost.
Ransomware has always had a human in the loop — someone at the keyboard, or at least someone who wrote the script. JADEPUFFER breaks that assumption: the first case the Sysdig Threat Research Team assesses to be a complete, end-to-end ransomware operation driven by a large language model, with no human issuing commands during the attack.
From a single unauthenticated RCE in an internet-facing Langflow instance (CVE-2025-3248), the agent enumerated the host, harvested credentials, looted an internal MinIO store, established persistence, then pivoted to its real target: a production server running MySQL and Alibaba Nacos. There it forged Nacos tokens, injected a backdoor admin, probed for a container escape, encrypted 1,342 configuration items, and dropped databases — chaining 600+ distinct payloads, diagnosing its own failures and fixing them in as little as 31 seconds.
This session walks the full kill chain using the actual captured payloads, then focuses on defenders: the four independent lines of evidence that it was machine-driven, and how to turn the agent's habit of narrating its own intent into detection and triage. Attendees leave with the IoCs, detection ideas, and hardening steps that would have broken this operation — and a realistic read on how the ransomware skill floor just collapsed.
Key takeaways
- Patch internet-facing AI-agent frameworks like Langflow promptly; a fixed CVE stayed exploitable on over 1,100 exposed instances more than a year after the patch shipped.
- Detect behavior, not payloads: an LLM-driven attacker chains new payloads and self-corrects, so signature-based detection on any single payload will miss it.
- Look for the absence of retry loops and rapid, correct recovery from format errors (for example, switching cleanly from JSON to XML) as evidence of an automated, LLM-driven actor rather than a human operator.
- Back up machine-learning models and weights with the same discipline as databases; replacing a model can cost tens of thousands to half a million dollars.
- Treat an agent's habit of narrating its own steps as a temporary detection and triage advantage, and assume attackers will suppress it once they realize it exposes them.
Speakers
Jake Walker
Jake Walker is a Principal Sales Engineer at Sysdig with over eight years in cybersecurity across Sysdig, Tenable, and Check Point. He partners closely with the Sysdig Threat Research Team, translating emerging cloud and AI-driven threats into… Read moreRead less
Jake Walker is a Principal Sales Engineer at Sysdig with over eight years in cybersecurity across Sysdig, Tenable, and Check Point. He partners closely with the Sysdig Threat Research Team, translating emerging cloud and AI-driven threats into practical detection and response for security teams. He presents this session on behalf of the Sysdig TRT, whose investigation of JADEPUFFER forms its foundation.